
Money worries weigh on critical infrastructure amid growing cyber threats, report finds
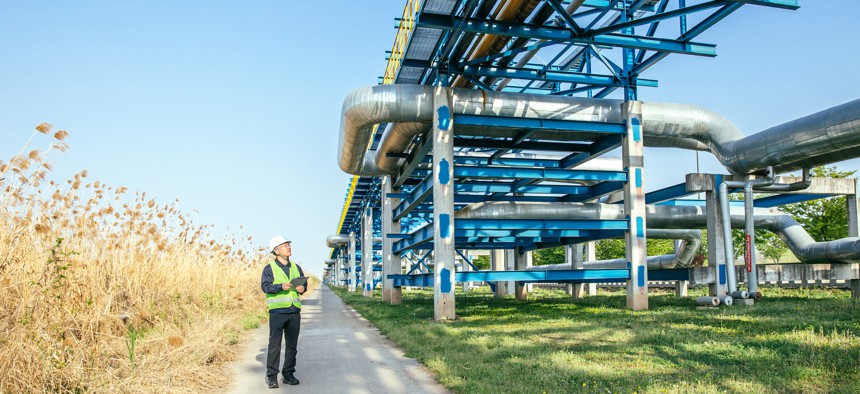
very good via Getty Images

 By
Chris Teale
A joint survey found that while almost all state tech leaders are worried about cyberattacks, they lack the funding to protect some of these crucial systems.
State technology leaders are almost universally concerned about cyberattacks on their critical infrastructure, but they lack the budget or resources to combat those attacks, a survey found last week.
Ninety percent of state chief information officers identified cyberattacks against critical infrastructure as a high concern, according to a joint survey by the National Association of State Chief Information Officers and General Dynamics Information Technology, released weeks before the former’s annual conference in San Diego. But only 65% of state CIOs’ budgets include funding to protect critical infrastructure, the study found, with those numbers likely even lower among the local governments and special districts that operate those systems.
Indeed, 22% said they have no funds dedicated to protecting critical infrastructure, although the report also noted that, in some instances, the CIO’s organization may not be responsible for protecting critical infrastructure. Instead, emergency management, environmental protection or homeland security are responsible for that work, the report said.
“On the one hand, we have this very high level of concern, and on the other hand, we have about two-thirds of the state agencies at the executive branch level funding protection for critical infrastructure,” said Mischa Beckett, senior director of cyber threat intelligence at GDIT. “That gap is what really sticks out to me as being noteworthy.”
There is evidence, however, of a growing awareness of the need to protect critical infrastructure and have state-led coordination of that effort. Of those surveyed, 73% said they include critical infrastructure protection as part of their whole-of-state cybersecurity plan, which involves comprehensive threat sharing, collaboration between the different levels of government and the private sector and better sharing of services.
“I think some of the mentality and some of the funding at the state level is changing,” Beckett said. “States are recognizing that their state critical infrastructure overlaps with locality critical infrastructure and overlaps with the private sector. This is a team sport, and so there's increased recognition of that and a movement to threat data, and we’re starting to see more and more that states are offering some cyber services to localities on down.”
The recent cyberattacks on water systems in Minnesota and other states by hackers affiliated with Iran highlighted just how vulnerable critical infrastructure is, and spurred federal action with the Project Watershed 250. That effort, which will initially pilot in Texas, will stress-test utilities over a six-month period to find cybersecurity vulnerabilities and help address them.
Amid stretched resources, Beckett said that initiative will help determine the best path forward for supporting critical infrastructure in strengthening cybersecurity. Whether that means low-cost information sharing, help from the private sector, grants or something else remains to be seen, especially as it needs to be resilient and not subject to short-term funding whims.
“I think that's going to be a really interesting chance to see what's effective in helping this,” she said. “Does that private-public partnership work really well? Are there things we can learn from a six-month pilot about what is effective and what is not so effective? How can we think about how to maximize low-cost or free resourcing given that we can't just magically create a ton of extra funding to satisfy everybody's needs?”
Instability at the federal level weighs heavily, however. Workforce cuts at the Cybersecurity and Infrastructure Security Agency, coupled with the removal of federal funding for the Multi-State Information Sharing and Analysis Center, mean states and localities may feel they have fewer partners in the federal government to help them identify and mitigate threats.
Meanwhile, future funding and authorization for the wildly popular State and Local Cybersecurity Grant Program remains up in the air. And the effects of all that uncertainty will be felt by states, localities and their critical infrastructure operators.
“There is growing apprehension that the progress made through whole‑of‑state programs may stall or collapse without sustained federal investment, pushing states to explore legislative appropriations and sector‑specific grants to maintain essential services,” the report says. “States have limited resources and funding mechanisms to offer [critical infrastructure cyber protection] outside of executive branch agencies and federal support is crucial to assisting vulnerable localities and other critical infrastructure sectors.”